Help & Support
SEARCH
Google fortifies Android against financial cybercrime
SHARE IT
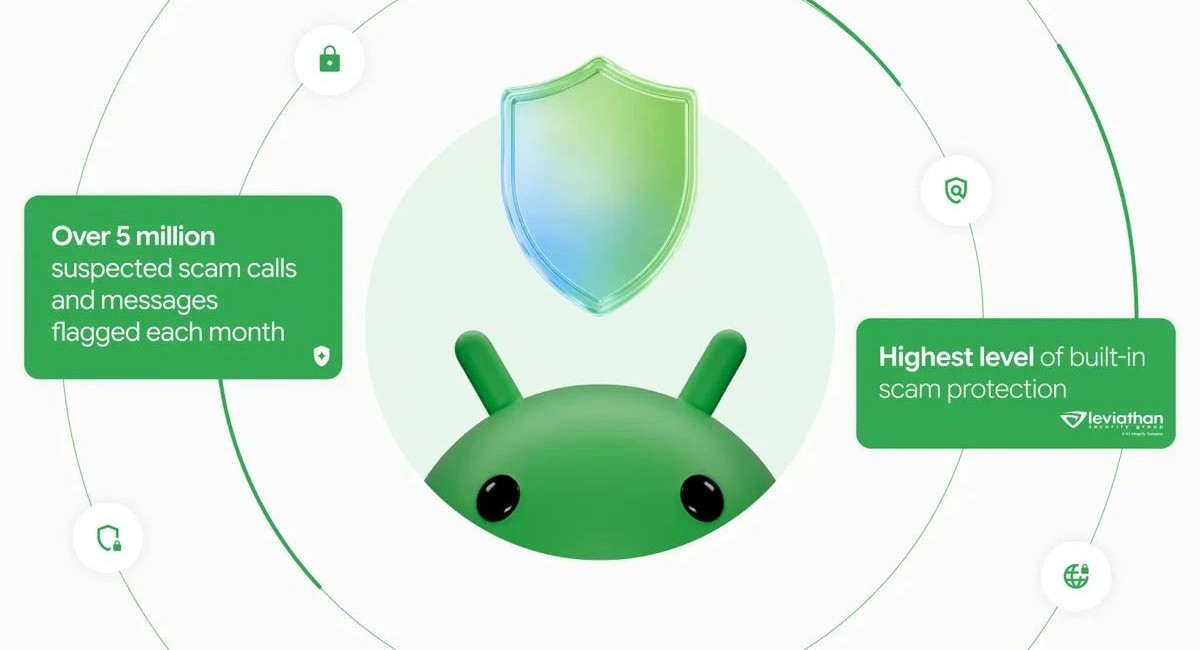
Modern smartphone fraud has outgrown predictable automated robocalls and rudimentary phishing attempts. Today,mobile scams operate as intricate social engineering enterprises that leverage spoofed identifiers, fabricated banking notifications, and generative voice cloning to deceive unsuspecting victims. As these deceptive tactics grow increasingly convincing and difficult for everyday consumers to discern, Google is rolling out an extensive suite of defense mechanisms embedded directly within Android to intercept digital threats before they can inflict financial harm.
Central to this defensive overhaul is the Enhanced Protection Mode within Google Messages. Cybercriminals frequently conceal their true objectives behind protracted, casual conversations, patiently nurturing trust before initiating an exploit. To dismantle this scheme, Google Messages harnesses advanced cloud-based Gemini artificial intelligence models to scrutinize the nuanced context of exchanges originating from unknown numbers. Operating via Private AI Compute, the architecture analyzes interaction patterns and identifies malicious intent while maintaining end-to-end privacy, ensuring user correspondence remains strictly inaccessible even to Google.
At the same time, localized machine intelligence provides an immediate second layer of defense. Running natively on the device hardware, Gemini Nano inspects unfamiliar website links in real time. While standard defensive databases reliably blacklist documented phishing destinations, fraudsters continually register fresh domains that temporarily evade security indexes. Gemini Nano bridges this vulnerability by synthesizing real-time web indicators before the user ever taps a URL, introducing redesigned visual checkpoints that prevent accidental navigation to hostile environments.
Beyond messaging protocols, Google has introduced countermeasures to neutralize vulnerabilities that emerge during routine phone usage, notably screen sharing. While sharing a display is standard practice for remote collaboration or family technical support, it introduces catastrophic exposure when entering credentials or payment details. Android previously masked sensitive interfaces inside native software, but the operating system now extends automatic redaction to Chrome and Android WebView. Whenever screen sharing is active, authentication forms and banking panels automatically black out on the observer display, preventing real-time surveillance of private financial information.
A parallel vector targeted by this security upgrade involves covert telecommunication tampering, specifically the diversion of incoming phone calls. Fraudsters frequently endeavor to reroute calls to capture SMS-based one-time passcodes, subsequently compromising authenticated banking portals. Android systematically restricts unvetted applications from silently altering call-forwarding rules in the background. Furthermore, should an adversary trick a user into manually entering a carrier MMI forwarding code into the dialer, the handset halts the execution with a conspicuous prompt, clarifying the security risks before the redirection takes effect.
Finally, Google is directly confronting financial impersonation by collaborating with leading international banking institutions. Through verified financial call frameworks, incoming communications from legitimate financial entities receive cryptographic validation in real time. Concurrently, real-time threat notifications and proactive call screening protocols are expanding beyond Pixel hardware, bringing coordinated protection against banking fraud to tens of millions of devices produced by Xiaomi, Motorola, OnePlus, and other Android partners.
MORE NEWS FOR YOU